Capability 01
AI Governance, Security & Compliance
Set the rules for enterprise AI, then enforce them in the architecture.
An AI system may have access to documents, databases, APIs and business processes. That makes its security boundary broader than the language model alone. We help organizations establish governance and security controls at the application, model gateway, retrieval, orchestration and tool execution layers.
Our work can include:
- AI inventory and risk classification: document AI applications, models, agents, owners, providers, data flows, business purposes, model versions, critical dependencies and risk levels.
- Identity and authorization: implement RBAC, ABAC, least privilege, SSO and enterprise identity integration, with delegated user identity or scoped service identities where appropriate.
- Data governance: define allowable data classes, handling rules, retention, encryption, residency, masking, redaction and restricted-context policies for prompts, retrieval and logs.
- Agent and tool permissions: scope what an agent may read, write, send or execute; apply allowlists, parameter validation, transaction limits, segregation of duties and policy checks before tools run.
- Model and supplier governance: review model provenance, deployment choices, licensing, hosting, third-party processing boundaries, change exposure and fallback dependencies.
- AI threat modeling: assess prompt injection, sensitive information disclosure, excessive agency, retrieval poisoning, insecure tool outputs, unbounded consumption and AI supply chain risks.
- Compliance control mapping: translate applicable enterprise controls and external frameworks into control objectives, owners, test methods and evidence requirements.
- Operational governance: design exception registers, model approval workflows, incident responsibilities, risk acceptance and scheduled control reviews.
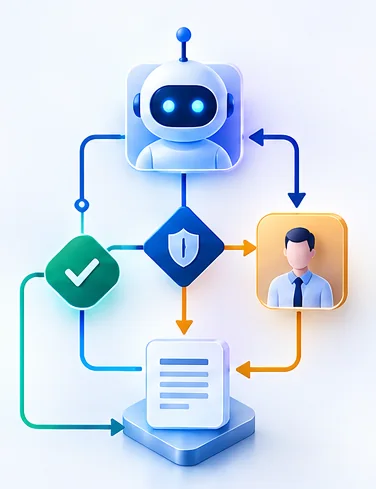
In practical terms, a customer service assistant may be permitted to retrieve an approved policy article but not read an unrelated employee record. A finance agent may prepare an adjustment for review but not post it to an ERP ledger. Those rules need to be enforced by the underlying systems and policy engine, not simply requested from the model.
We can align governance designs with relevant references such as NIST AI RMF, NIST's Generative AI Profile, ISO/IEC 42001 and the OWASP GenAI LLM Top 10, as appropriate. Alignment supports the organization's governance program; it is not a claim of certification or guaranteed regulatory compliance.
What this delivers: An AI control framework supported by technical enforcement points, system ownership and evidence that can be tested.